TPM 中漏洞的 BitLocker 缓解计划

应用对象
Windows 10, version 1703, all editions Windows Server 2016 Windows Server 2016 Essentials Windows Server 2016 Standard Windows 10 Windows 10, version 1511, all editions Windows 10, version 1607, all editions Windows Server 2012 R2 Datacenter Windows Server 2012 R2 Standard Windows Server 2012 R2 Essentials Windows Server 2012 R2 Foundation Windows 8.1 Enterprise Windows 8.1 Pro Windows 8.1 Windows RT 8.1 Windows Server 2012 Datacenter Windows Server 2012 Standard Windows Server 2012 Essentials Windows Server 2012 Foundation Windows Server 2008 R2 Service Pack 1 Windows Server 2008 R2 Datacenter Windows Server 2008 R2 Enterprise Windows Server 2008 R2 Standard Windows Server 2008 R2 Web Edition Windows Server 2008 R2 Foundation Windows 7 Service Pack 1 Windows 7 Ultimate Windows 7 Enterprise Windows 7 Professional Windows 7 Home Premium Windows 7 Home Basic Windows 7 Starter Windows Vista Service Pack 2 Windows Vista Home Basic Windows Vista Home Premium Windows Vista Business Windows Vista Ultimate Windows Vista Enterprise Windows Vista Starter Windows Server 2008 Service Pack 2 Windows Server 2008 Foundation Windows Server 2008 Standard Windows Server 2008 for Itanium-Based Systems Windows Server 2008 Web Edition Windows Server 2008 Enterprise Windows Server 2008 Datacenter

摘要

某些受信任的平台模块 (TPM) 芯片组中存在安全漏洞。 此漏洞削弱了关键力量。

本文有助于识别和解决受 Microsoft 安全通报ADV170012中所述漏洞影响的 BitLocker 受保护设备中的问题。

详细信息

概述

本文档介绍如何纠正基于 BitLocker TPM 的保护程序中的漏洞影响。

必须根据相关机密的保护方式来查看对其他 BitLocker 保护程序方法的影响。 例如,如果用于解锁 BitLocker 的外部密钥受到 TPM 保护,请参阅 公告 来分析影响。 本文档不在对漏洞的这些影响进行补救的工作范围。

如何识别影响

BitLocker 将 TPM 密封和解封操作与存储根密钥一起用于保护操作系统卷上的 BitLocker 机密。  此漏洞影响 TPM 1.2 上的密封和解封操作,但不会影响 TPM 2.0 上的操作。

当使用基于 TPM 的保护程序来保护操作系统卷时,仅当 TPM 固件版本为 1.2 时,才会影响 BitLocker 保护的安全性。

要标识受影响的 TPM 和 TPM 版本,请参阅“2. 确定组织中受影响的设备“ Microsoft安全通报ADV170012中的”建议的操作“。

若要检查 BitLocker 状态,请以计算机管理员身份在命令提示符下运行“manage-bde -status <OS volume letter:”>。
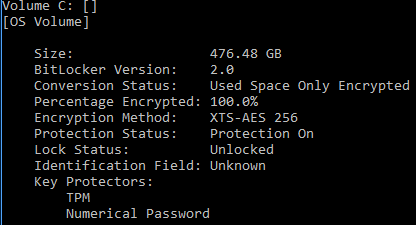
图 1:同时受 TPM 保护程序和 RecoveryPassword 保护程序保护的操作系统卷的示例输出

图 1 同时受 TPM 保护程序和恢复密码保护程序保护的操作系统卷的示例输出。 (设备加密不受此 TPM 漏洞的影响。)

修复固件更新后的 BitLocker 漏洞

按照以下步骤修正此漏洞:

  1. 暂停 BitLocker 保护:以计算机管理员身份运行“manage-bde -protectors <OS volume letter:> –disable”。
  2. 清除 TPM。 有关说明,请参阅“6. 清除 TPM“ ADV170012 Microsoft。
  3. 重启 Windows 8 和更高版本的 Windows 后,BitLocker 保护会自动恢复。 对于 Windows 7,请以计算机管理员身份运行“manage-bde -protectors <OS volume letter:> –enable”以恢复 BitLocker 保护。

以下页面提供了 manage-bde.exe 的完整命令行参考:

https://technet.microsoft.com/en-us/library/ff829849 (v=ws.11) .aspx